How to Change Nameservers Without Downtime (Step-by-Step, 2026)
Short answer: recreate every DNS record at the new provider first, remove the old DNSSEC DS record (or migrate DNSSEC properly), then replace the nameservers at your registrar. Keep the old DNS zone running unchanged for at least 48 hours. Done in that order, visitors and email see no gap, because old and new nameservers give the same answers while caches expire.
Step 1: Inventory your current records
Export or list every record at the current DNS host: A and AAAA (website), CNAME (www, subdomains, verification), MX (mail), TXT (SPF, DKIM, DMARC, site verifications), SRV and CAA. Many providers have a zone export (BIND format). The most common outage after a nameserver change is a forgotten MX or DKIM record, which silently breaks email. Our DNS Lookup tool shows the live records for a quick cross-check.
Step 2: Build the zone at the new provider
Add the domain at the new DNS host and enter or import the same records. Some providers (Cloudflare among them) scan your existing records automatically. Treat that scan as a starting point and compare it line by line with your inventory. The new provider will then show you the nameserver names to use, for example two hostnames ending in ns.cloudflare.com (see Cloudflare's full-setup guide).
Before switching, test the new zone directly against the new servers:
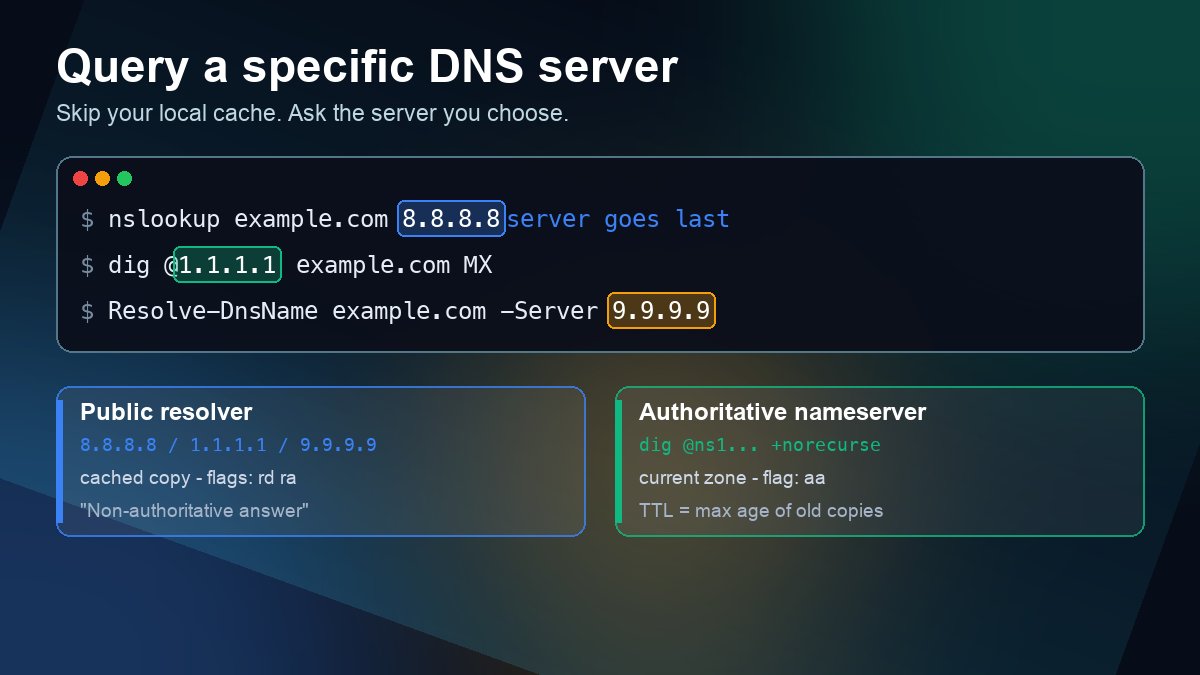
dig @NEW-NS-1 example.com A +short
dig @NEW-NS-1 example.com MX +short
dig @NEW-NS-1 example.com TXT +short
Step 3: Handle DNSSEC before you switch
If the domain is DNSSEC-signed, the registry holds a DS record that matches the old provider's signing key. Point the domain at new nameservers that sign with a different key (or don't sign at all) and validating resolvers will return SERVFAIL: the domain disappears for a large share of users. The simple, safe path: remove the DS record at the registrar, wait for its TTL to pass (often a day or two), switch nameservers, then enable DNSSEC at the new provider and add its new DS record (see Cloudflare's DNSSEC docs for that last step). Not sure whether the domain is signed? Our guide on how to check DNSSEC shows the one-line test.
Step 4: Change the nameservers at your registrar
The setting always lives with the company where the domain is registered, not necessarily your web host. Menus change from time to time, so follow the registrar's own help page if the labels differ:
- GoDaddy: Domain Portfolio, select the domain, DNS, Nameservers, Change Nameservers, then choose "I'll use my own nameservers." (GoDaddy help)
- Namecheap: Domain List, Manage, Nameservers, select "Custom DNS," enter each name and save with the green check mark. (Namecheap help)
- Squarespace Domains (where former Google Domains registrations moved): Domains, select the domain, DNS, Domain Nameservers, Use Custom Nameservers. (Squarespace help)
- Cloudflare Registrar: domains registered with Cloudflare must use Cloudflare's nameservers, so to use another DNS host you first transfer the domain to another registrar.
Enter the names exactly as the new provider gave them, with no trailing spaces, and remove every old entry. Mixing old and new nameservers sends visitors to two different zones at random.
Step 5: Verify at the registry, not just your browser
The registry usually publishes the change within minutes. Check it directly, bypassing caches:
dig @a.gtld-servers.net example.com NS +norecurse   # .com and .net
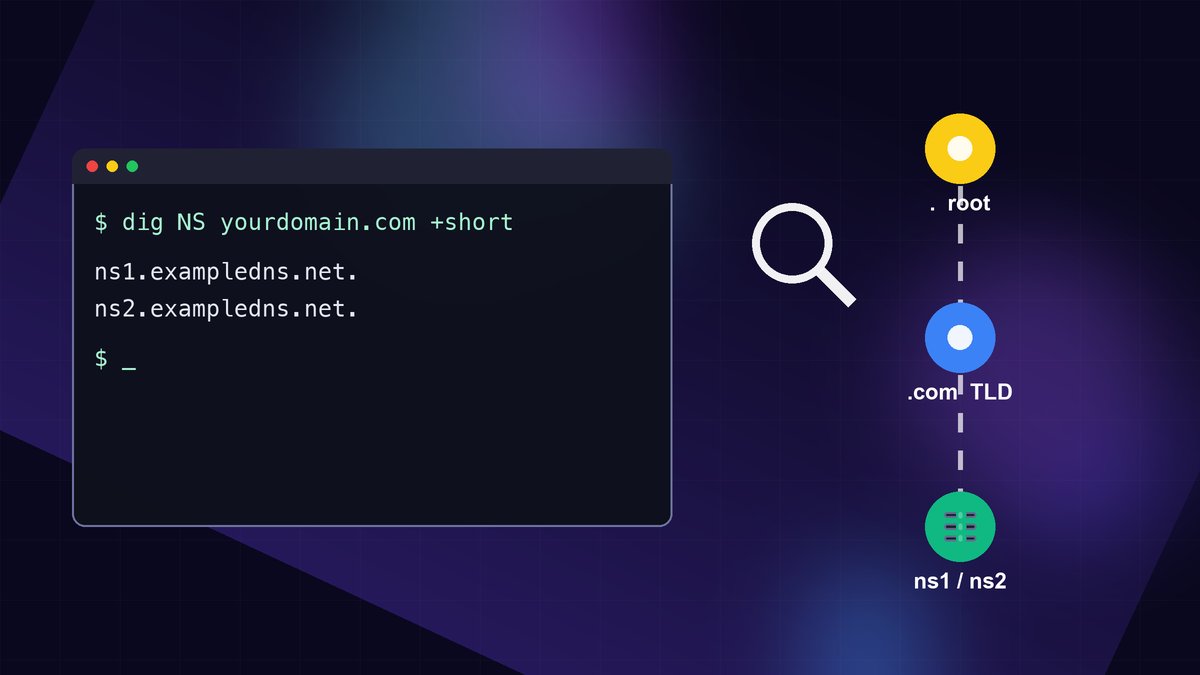
dig NS example.com +trace                            # any TLD
If the registry already shows the new names, you are done; the rest is caching. Resolvers that cached the old delegation keep using it until it expires. For .com and .net, the delegation NS records carry a 48-hour TTL (172,800 seconds), which is why the old zone must stay up. Our Nameserver Lookup tool shows what public resolvers return right now.
Step 6: Clean up after 48 hours
- Send a test email to and from the domain and check SPF, DKIM and DMARC results in the received headers.
- Re-verify services that check DNS (Google Search Console, Microsoft 365, email-marketing platforms).
- Enable DNSSEC at the new provider and add the new DS record at the registrar if you removed it in step 3.
- Only then delete the zone at the old provider.
Common mistakes
- Switching nameservers before copying MX and TXT records.
- Leaving an old DS record in place (instant SERVFAIL for validating resolvers).
- Changing nameservers at the web host instead of the registrar.
- Cancelling the old DNS plan the same day.
- Confusing nameservers with glue records: you only need glue when the nameservers are under your own domain.
Frequently asked questions
How long does a nameserver change take?
The registry usually updates within minutes to an hour. Resolvers that cached the old delegation can keep using it for up to the delegation TTL, which is 48 hours for .com and .net. Keep both old and new zones identical during that window and nobody notices the switch.
Will changing nameservers break my email?
Only if the new zone is missing records. Copy every MX record plus the TXT records for SPF, DKIM and DMARC before switching, then send a test message after the change.
Can I lower the TTL to make the switch faster?
You can lower the TTLs of your own records at the old provider ahead of time, but the NS delegation TTL is set by the registry (48 hours for .com), so plan for that window rather than trying to shorten it.
Do I need to change nameservers to point my domain at a new host?
Not always. If you only move the website, changing the A or CNAME record at your current DNS provider is enough. Change nameservers only when you want a different company to manage all of the domain's DNS.