What Are Nameservers and How Do They Work? (Plain-English Guide)
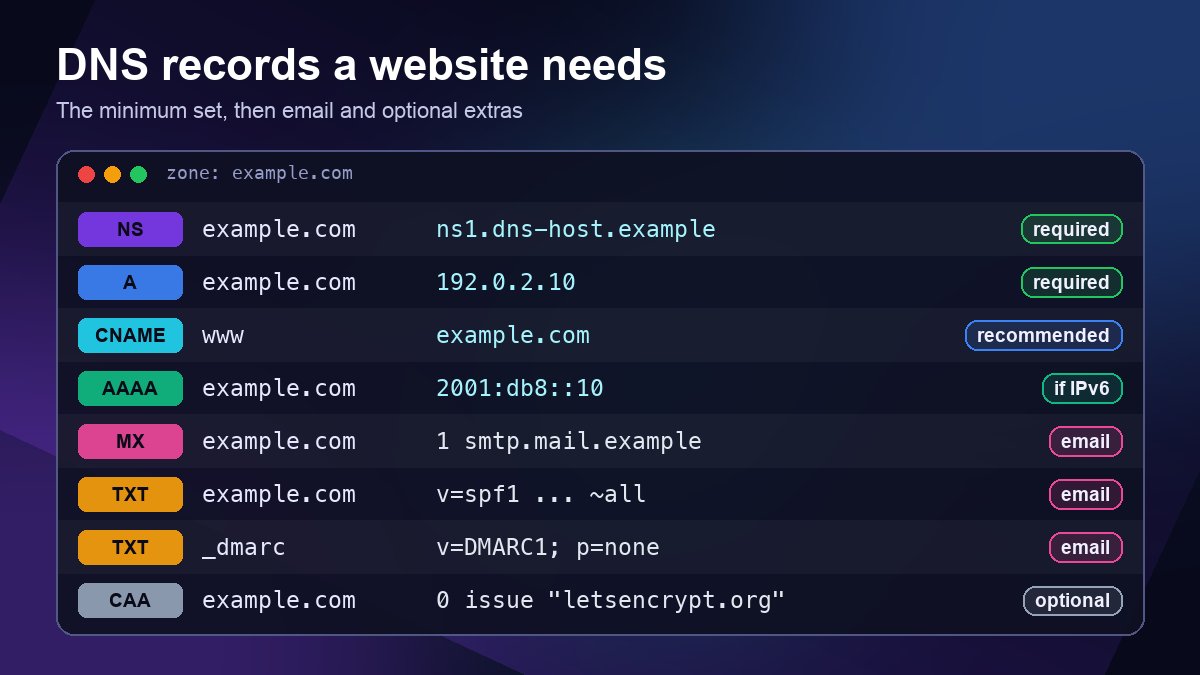
Short answer: a nameserver is a server that answers DNS questions for a domain. The nameservers listed for your domain at the registry are the authoritative source for its records (A, AAAA, CNAME, MX, TXT and so on). Whoever runs those nameservers (your registrar, Cloudflare, AWS Route 53, your web host) controls where your website and email point.
What a nameserver actually does
DNS turns names such as example.com into the data computers need, mainly IP addresses and mail routes. No single server knows every answer. Instead, DNS is a tree of delegations, defined in the original standards RFC 1034 and RFC 1035. Each level only knows which nameservers are responsible for the level below it.
When you set nameservers for your domain at your registrar, the registrar sends them to the registry for your top-level domain (Verisign runs .com and .net). The registry publishes them as NS records in the TLD zone. From then on, every resolver that asks about your domain is sent to those servers.
The four server roles in a lookup
- Recursive resolver. The server your device asks first: your ISP's resolver, your router, or a public one such as Google Public DNS (8.8.8.8) or Cloudflare (1.1.1.1). It does the legwork and caches answers.
- Root nameservers. The top of the tree. There are 13 root server identities, a.root-servers.net to m.root-servers.net, run by 12 independent operators (the list is published by IANA). Each identity is served by many anycast copies around the world; root-servers.org shows the live map. The root only says "for .com, ask these servers."
- TLD nameservers. For .com these are a.gtld-servers.net to m.gtld-servers.net. They hold the delegation: "for example.com, ask ns1.dnshost.example and ns2.dnshost.example."
- Authoritative nameservers. The servers you choose. They hold the zone file with your actual records and give the final answer.
Resolvers cache every step for as long as each record's TTL (time to live) allows, so most lookups never go all the way to the root.
Authoritative vs. recursive: the difference that matters
People mix these up constantly. An authoritative nameserver only answers for the zones it hosts and does not look anything else up. A recursive resolver answers anything by asking other servers and caching what it learns. When you "change your DNS" on a laptop to 1.1.1.1, you change your recursive resolver. When you "change your nameservers" at a registrar, you change who is authoritative for your domain. The two settings are unrelated.
Why a domain lists two or more nameservers
RFC 1034 asks for at least two nameservers per zone so the domain stays reachable if one fails, and most registries enforce a minimum of two. Good DNS providers go further and run each nameserver name on an anycast network in many locations.
Glue records, in one paragraph
If a domain's nameservers live inside the same domain (for example ns1.example.com serving example.com), a resolver would need to resolve example.com to find the server that resolves example.com. To break that loop, the registry also stores the IP addresses of those nameservers, called glue records. You only set glue ("register child nameservers" or "host records" in most registrar panels) when you run nameservers under your own domain.
How to check a domain's nameservers
The quickest way is our Nameserver Lookup tool. From a terminal:
dig NS example.com +short
nslookup -type=NS example.com
To see what the registry currently delegates to (useful right after a change, because it skips your resolver's cache), ask a .com TLD server directly:
dig @a.gtld-servers.net example.com NS +norecurseIf the registry answer and the answer from your usual resolver differ, the change is done and you are waiting for caches to expire. Our guide to DNS propagation explains how long that takes.
When you would change nameservers
- Moving DNS to a provider with a better network, DNSSEC support or an easier dashboard.
- Putting a site behind a CDN or proxy that requires its own nameservers (Cloudflare's full setup works this way).
- Switching web hosts that manage DNS for you.
Before switching, copy every record to the new provider first. The step-by-step version is in How to Change Nameservers.
Frequently asked questions
Are nameservers the same as DNS servers?
Nameservers are one kind of DNS server. The term usually means the authoritative servers that hold a domain's records. Recursive resolvers such as 8.8.8.8 or 1.1.1.1 are also DNS servers, but they look answers up for you instead of holding your zone.
How many nameservers should a domain have?
At least two, as RFC 1034 recommends and most registries require. Major DNS providers usually give you two to four names, each backed by many anycast servers.
Does changing nameservers move my website?
No. It only changes who answers DNS for the domain. Your site and email keep working only if the new nameservers have the same records (A, CNAME, MX, TXT) as the old ones, so copy them before you switch.
How do I find out who hosts a domain's DNS?
Look up its NS records with a nameserver lookup tool or dig NS example.com. The hostnames usually reveal the provider, for example *.ns.cloudflare.com or *.awsdns-*.com.